Security from your server log
Your access log already records every scanner that asks for your secret files. Skald reads it and tells you who is probing you, what they tried, and what applies to your stack.
Security in Skald
Your server log already shows who is probing you
Every request for /.env, /.git/config, a backup or a login page is a line in your access log. Skald reads that log, the same lines every other figure is counted from, and answers six questions, every figure counted twice.
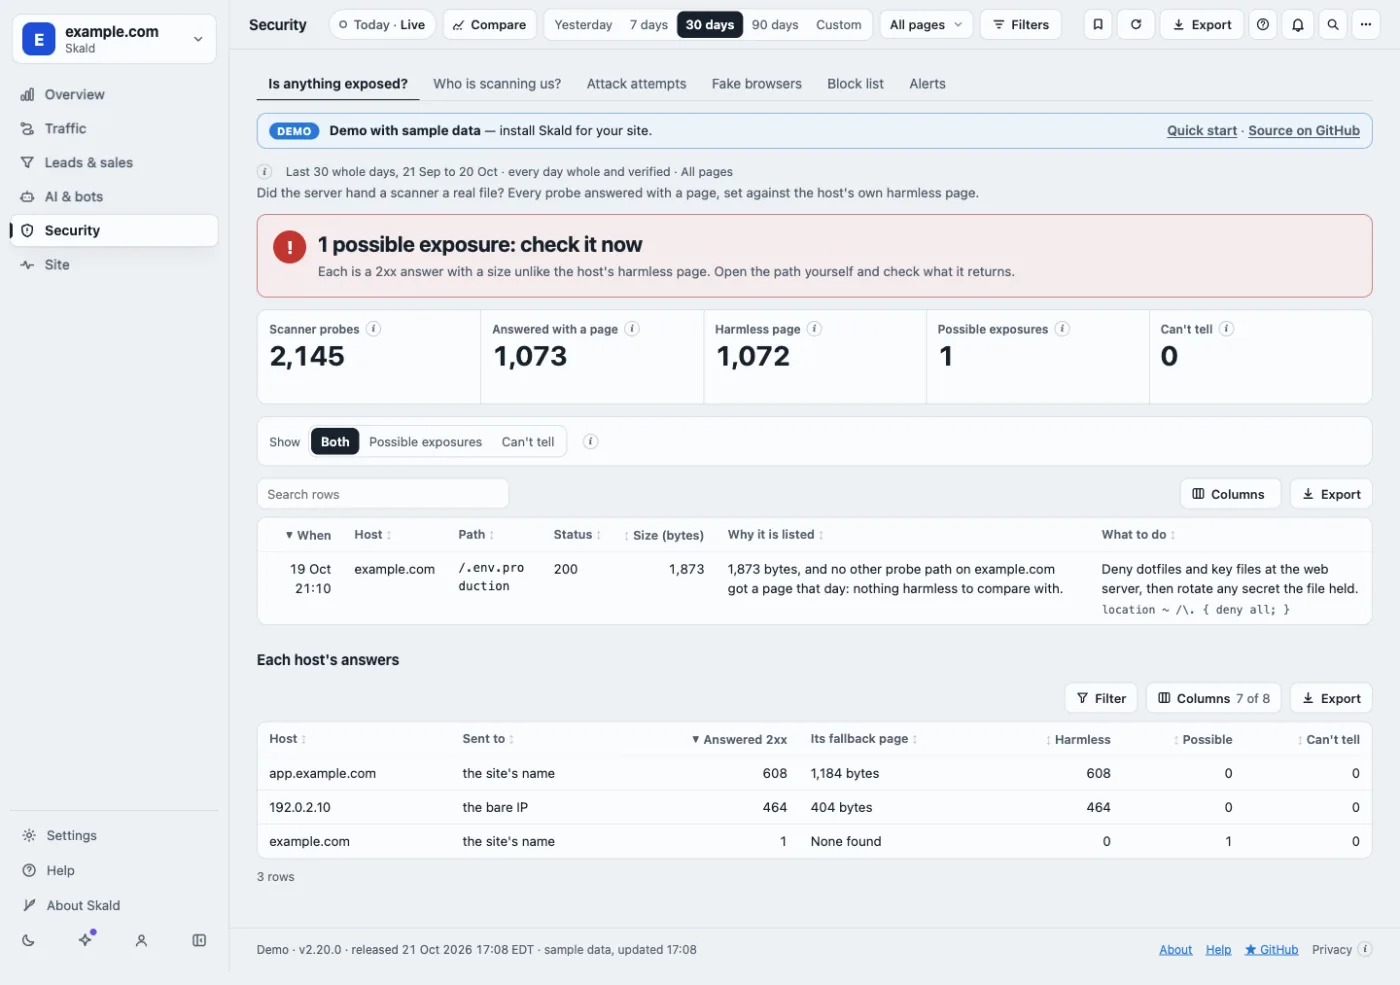
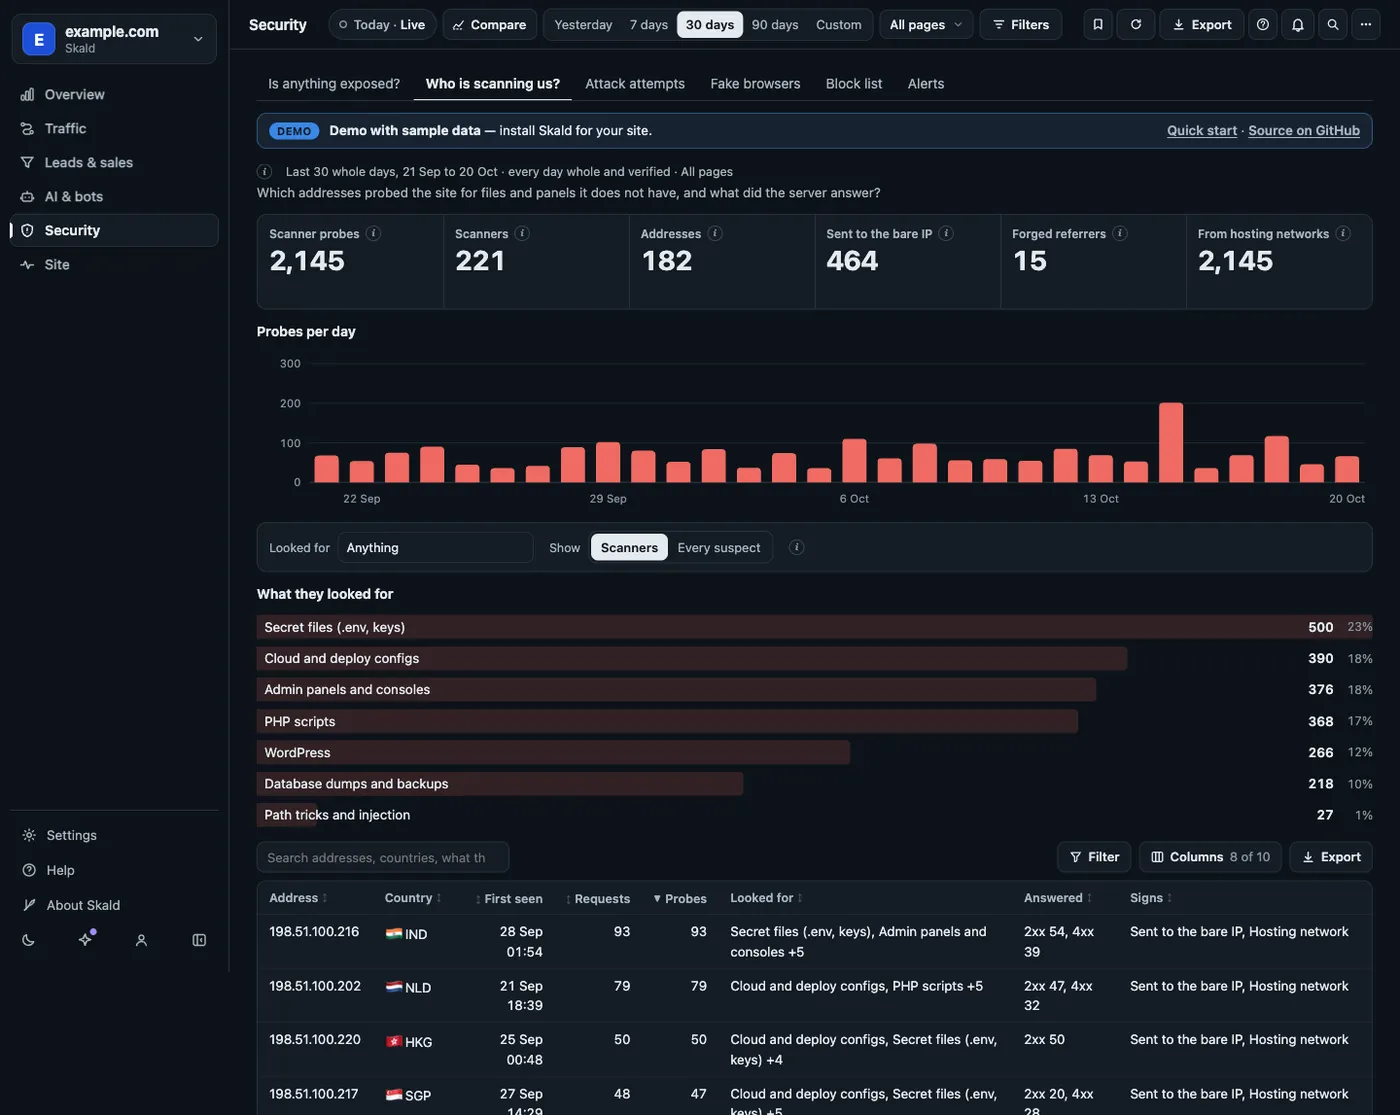
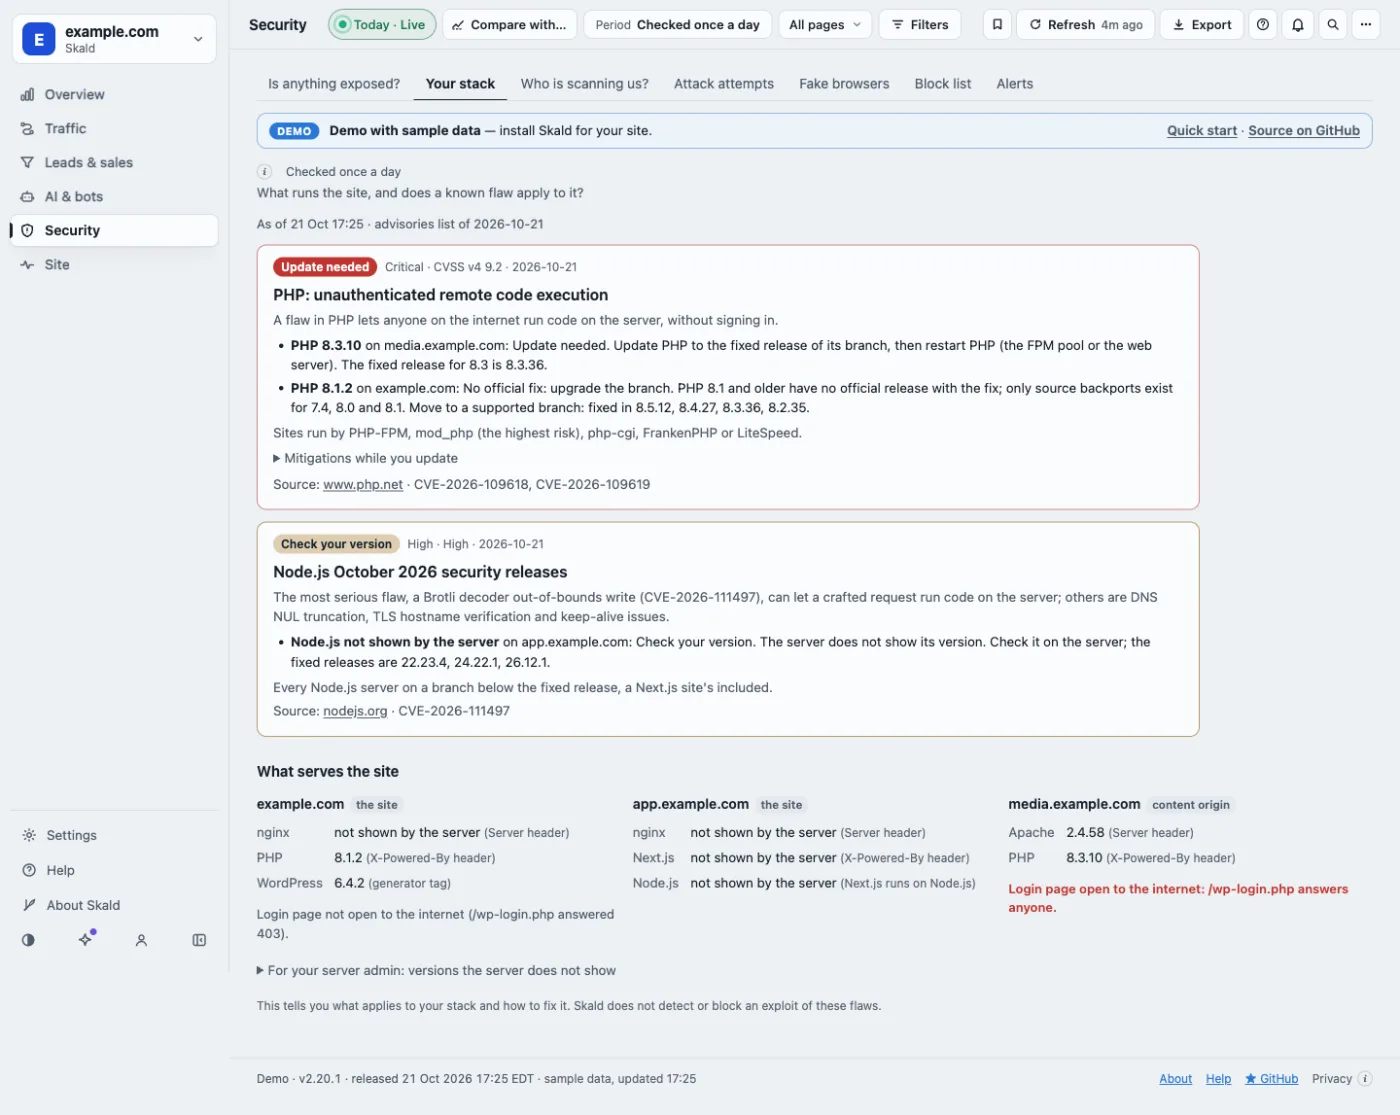
- Attack attempts: path tricks and injection in the address, login and form hammering, bursts.
- Fake browsers: agents that claim to be a browser but never load your site's files.
- Block list: the addresses to block, ready to paste into nginx, Cloudflare or fail2ban.
- Alerts: a possible exposure or an advisory for your stack, to the people on each site, at once or in the daily mail.
Skald tells you what applies and what was tried; it does not block attacks. Free to run on your own server, source-available (Elastic License 2.0). Your data, on your server, and you choose what is kept.
Live demo
Click around the real dashboard with sample data
Every section, 60 days of a made-up site. In your browser, nothing to install, no sign-up.
Hosted Skald
Start free. We set it up for you.
30 days free, no card. Your account is ready within one working day. Or run it yourself, free, with the install guide.